Shell, desktop and files
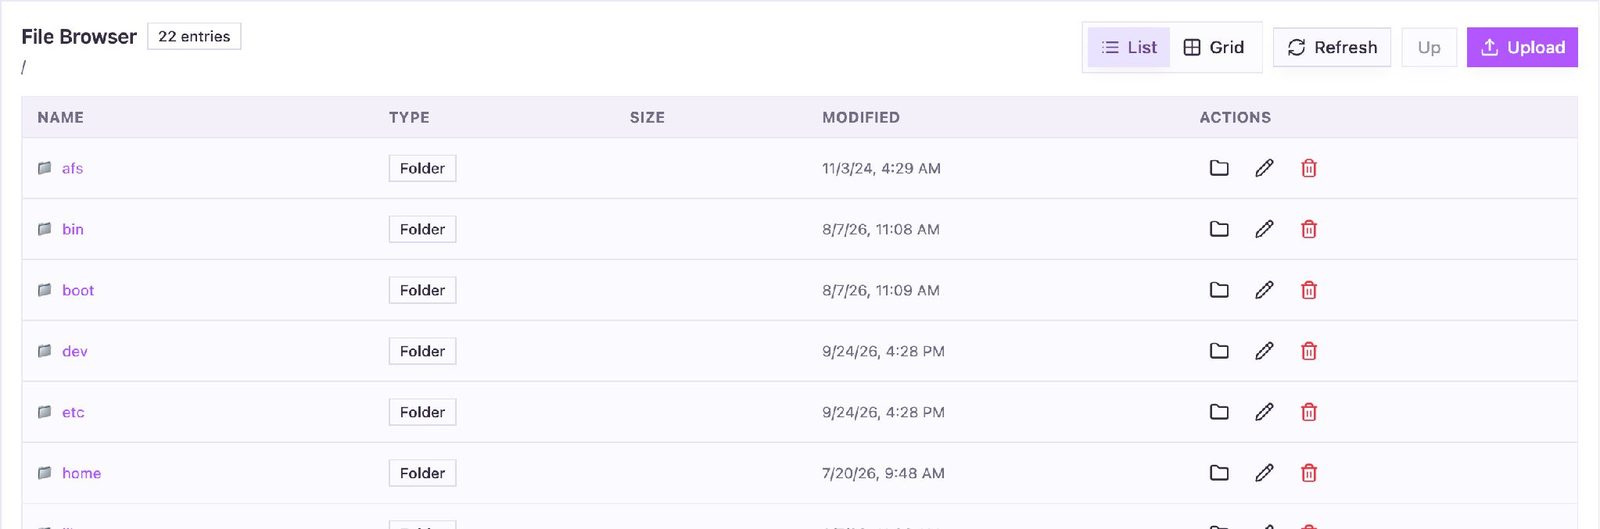
Browser-based shell, desktop and file sessions to Linux and Windows systems.
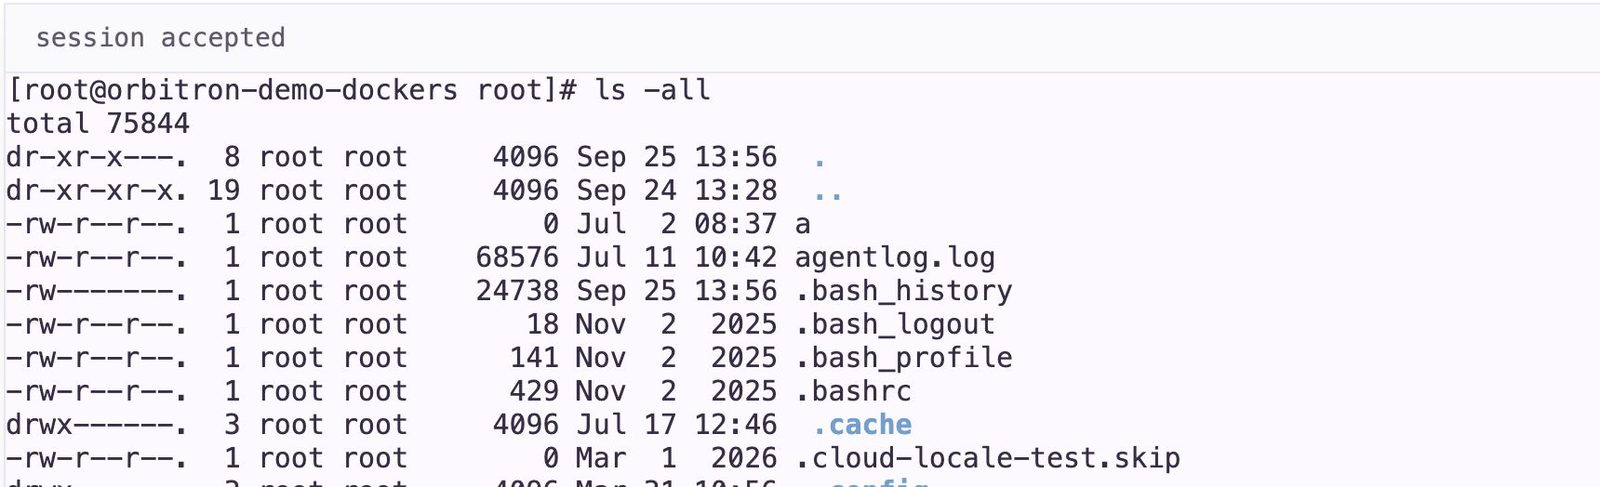
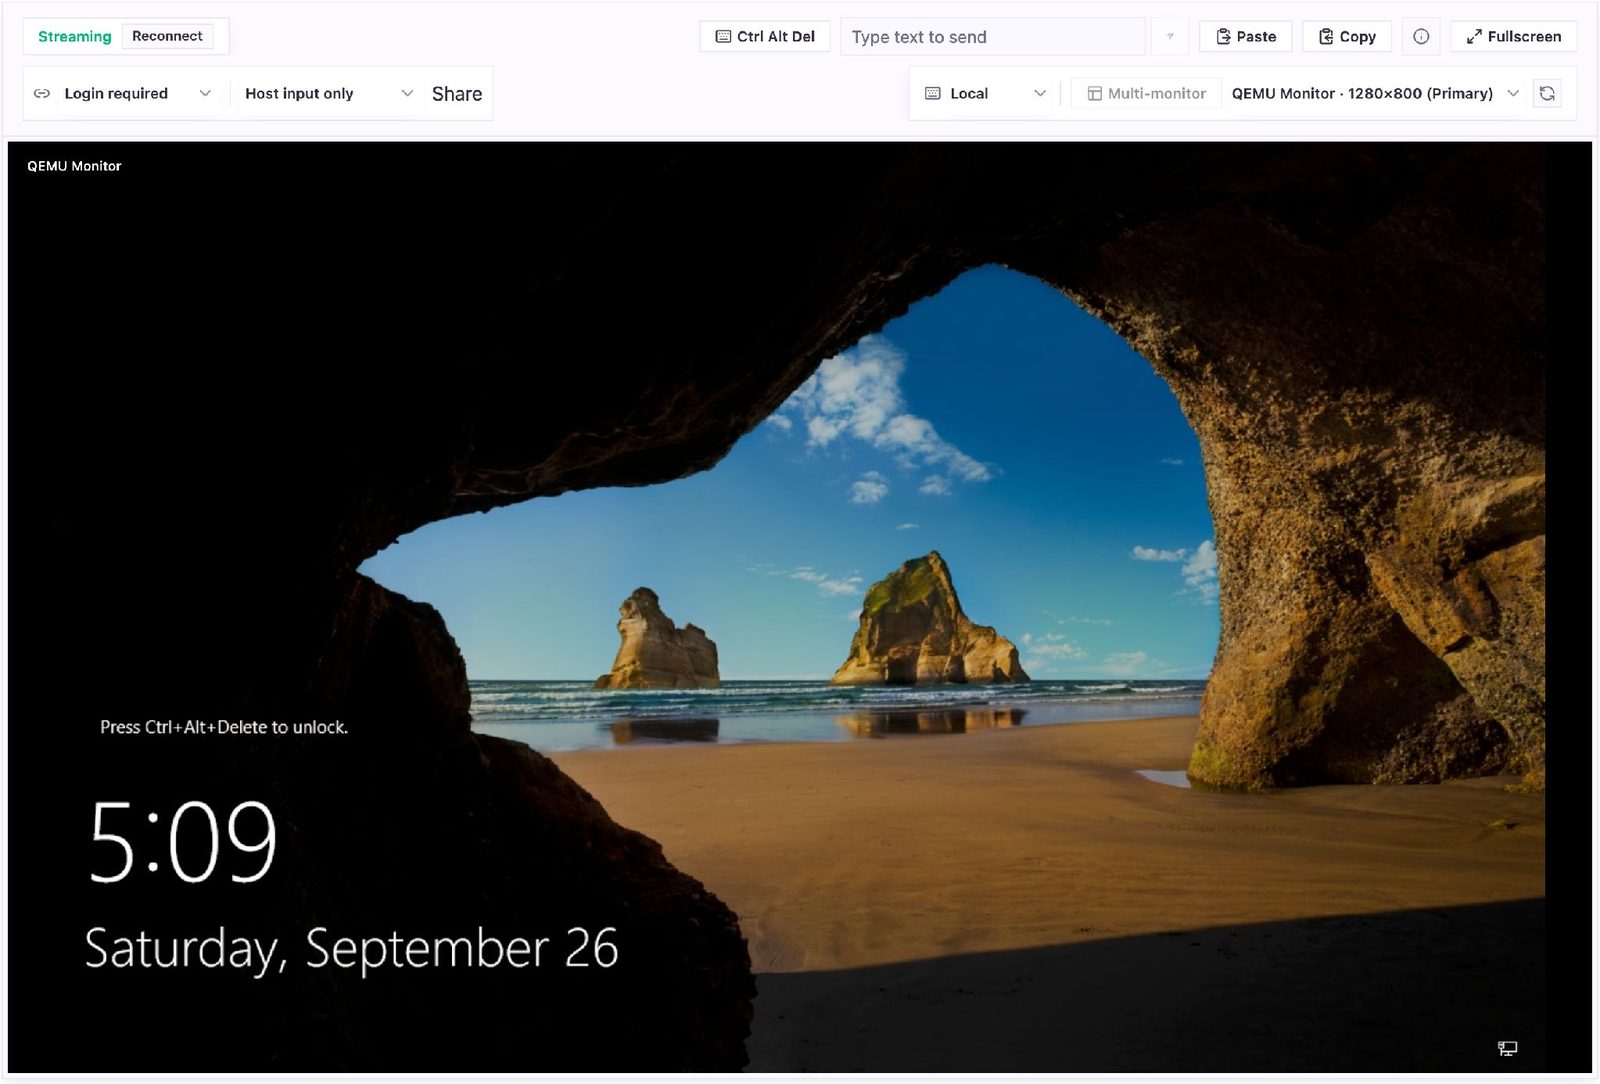
Open shell, desktop and file sessions to Linux and Windows systems through the Orbitron agent instead of open SSH, RDP or WinRM. Sessions are approved, recorded and replayable, credentials are injected from the vault and operators are unlimited.
Capabilities
Browser-based shell, desktop and file sessions to Linux and Windows systems.
Reach systems through the agent instead of opening SSH, RDP, WinRM or SMB to the network.
Access by user and asset, with approval steps and session duration controls.
Record sessions, replay them and end active sessions when needed.
Secrets and certificates are injected into sessions without being shown to operators.
License the systems you manage, not the people who manage them.
In the console
Built from Orbitron modules
Every Orbitron product is a set of platform modules on the same agent. Products you add later reuse the modules you already have.
 Remote ConnectionManagement · RCON
 Vault ManagementManagement · VAULT
 Command EngineAutomation · CMD
Optional add-ons
 Secure File Transfer
 Resolve (ITSM)
 Asset Visibility
 Endpoint Automation
Licensing
Per managed asset. Unlimited operators.
Annual subscription, priced for your environment. Products bought together share the modules they have in common.
Request pricingIncluded with every subscription
Works with
 Endpoint & IT OperationsOrbitron Unified Endpoint ManagementInventory, configuration and operations for every endpoint.
 Access & ServiceOrbitron Resolve ITSMA service desk that knows the device behind every request.
 Security OperationsOrbitron SOARAutomated response across agents, agentless targets and third-party tools.
Book a demo and we will show it on infrastructure like yours.