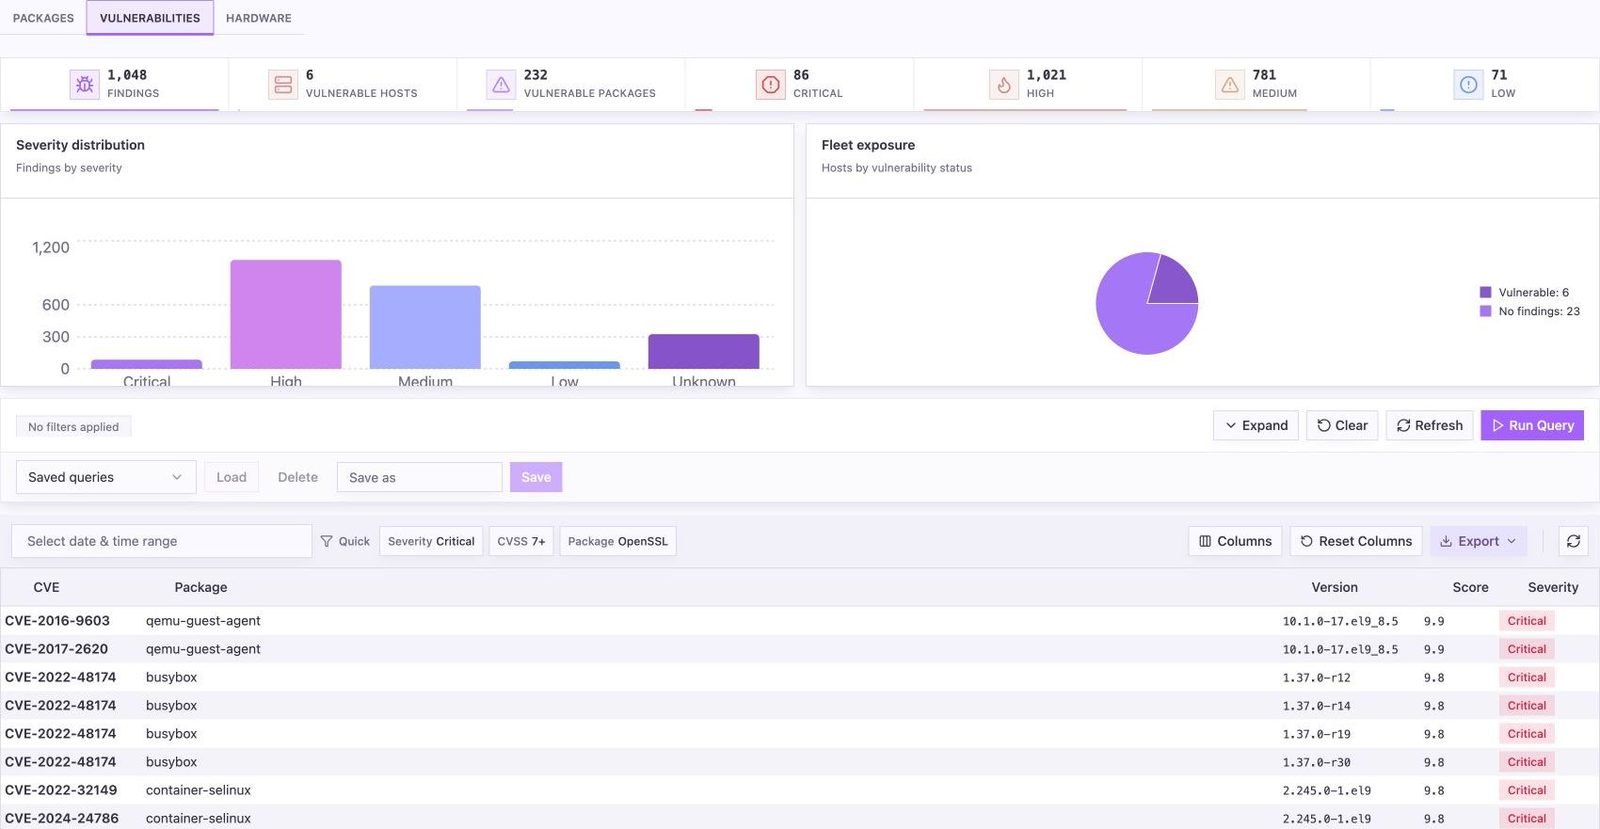
CVE, version and CVSS
Every finding shows the affected package, installed and fixed versions and severity.
Match installed packages and software versions against advisory data, see exactly which hosts, images and containers are exposed and fix what matters first.
Capabilities
Every finding shows the affected package, installed and fixed versions and severity.
Pivot between vulnerabilities, packages and assets to see blast radius at a glance.
One view across hosts and container workloads when container visibility is enabled.
Rank remediation by severity and the number and importance of affected assets.
Hand findings to Patch & Remediation and verify the fix after rollout.
Critical-only, by ecosystem or by host group, for quick answers to audit questions.
Built from Orbitron modules
Every Orbitron product is a set of platform modules on the same agent. Products you add later reuse the modules you already have.
 Vulnerability ManagementSecurity · VULN
 Asset VisibilityVisibility · AVIS
 Endpoint VisibilityVisibility · EVIS
Optional add-ons
 Container Visibility
 Cloud Visibility
 Patch Management
 Resolve (ITSM)
 Compliance Management
Licensing
Per assessed asset.
Annual subscription, priced for your environment. Products bought together share the modules they have in common.
Request pricingIncluded with every subscription
Works with
 Endpoint & IT OperationsOrbitron Patch & RemediationFind missing updates, roll them out in waves, verify every install.
 Security OperationsOrbitron Compliance PostureContinuous checks against CIS benchmarks and your own policies.
 Cloud & ContainerOrbitron Container SecurityImage risk, runtime detection and isolation for containers.
Book a demo and we will show it on infrastructure like yours.