CIS benchmarks
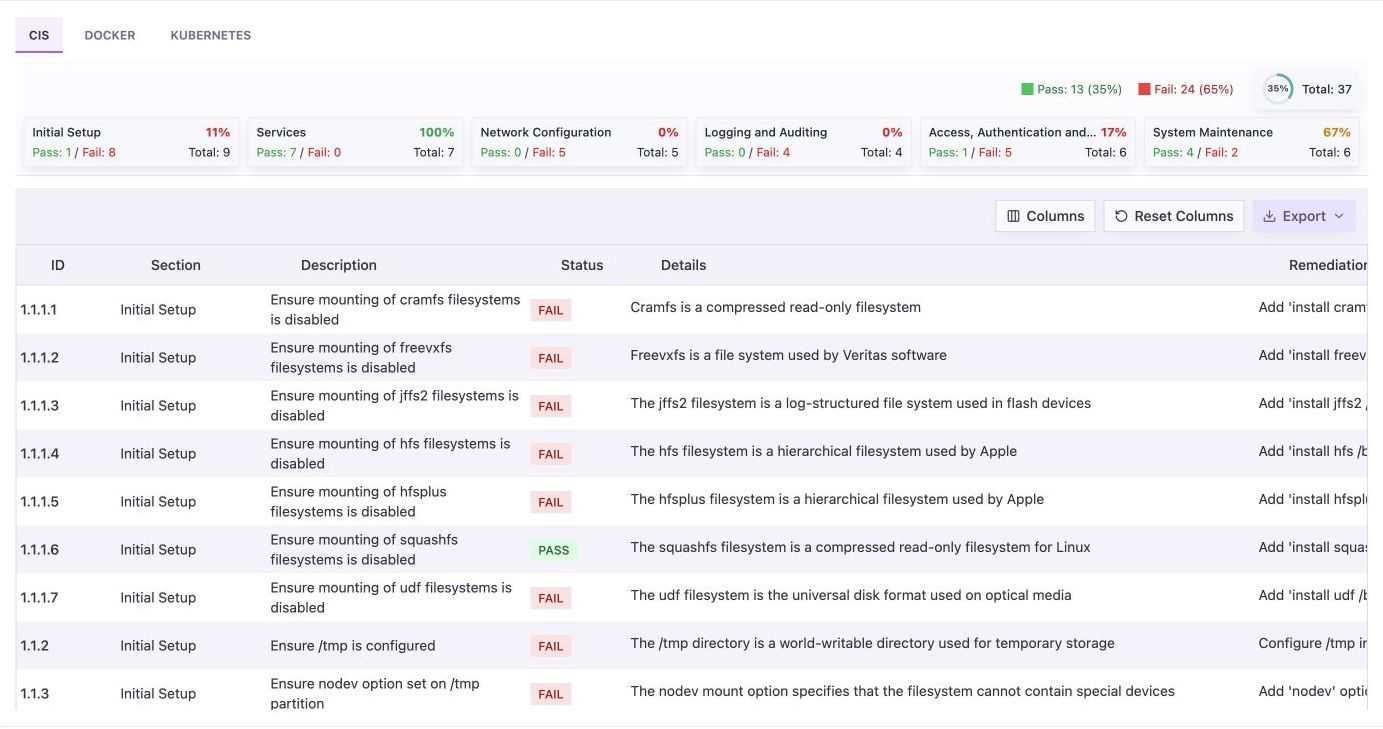
Built-in checks for operating systems, Docker and Kubernetes.
Continuously check hosts, containers and Kubernetes against CIS benchmarks and your own policies, keep the evidence and link every finding to a remediation command.
Capabilities
Built-in checks for operating systems, Docker and Kubernetes.
Define organization-specific technical controls with ConfigIron and track violations centrally.
Control results, history and exceptions kept for audits.
Each finding can point to a remediation command or playbook.
See when a system moves away from its approved configuration.
Benchmark and compliance reports for operations, security and governance teams.
Built from Orbitron modules
Every Orbitron product is a set of platform modules on the same agent. Products you add later reuse the modules you already have.
 Compliance ManagementSecurity · COMP
 Asset VisibilityVisibility · AVIS
 Endpoint VisibilityVisibility · EVIS
Optional add-ons
 Container Visibility
 Container Security
 Cloud Visibility
 Cloud Security
 Alert Management
 Endpoint Automation
Licensing
Per assessed asset.
Annual subscription, priced for your environment. Products bought together share the modules they have in common.
Request pricingIncluded with every subscription
Works with
 Security OperationsOrbitron Risk-Based Vulnerability ManagementCritical findings mapped to the systems they affect.
 Cloud & ContainerOrbitron Cloud Security PostureMisconfigurations across AWS and Azure, ranked by severity.
 Endpoint & IT OperationsOrbitron Patch & RemediationFind missing updates, roll them out in waves, verify every install.
Book a demo and we will show it on infrastructure like yours.