AWS and Azure visibility
Accounts, regions and resources in a normalized inventory.
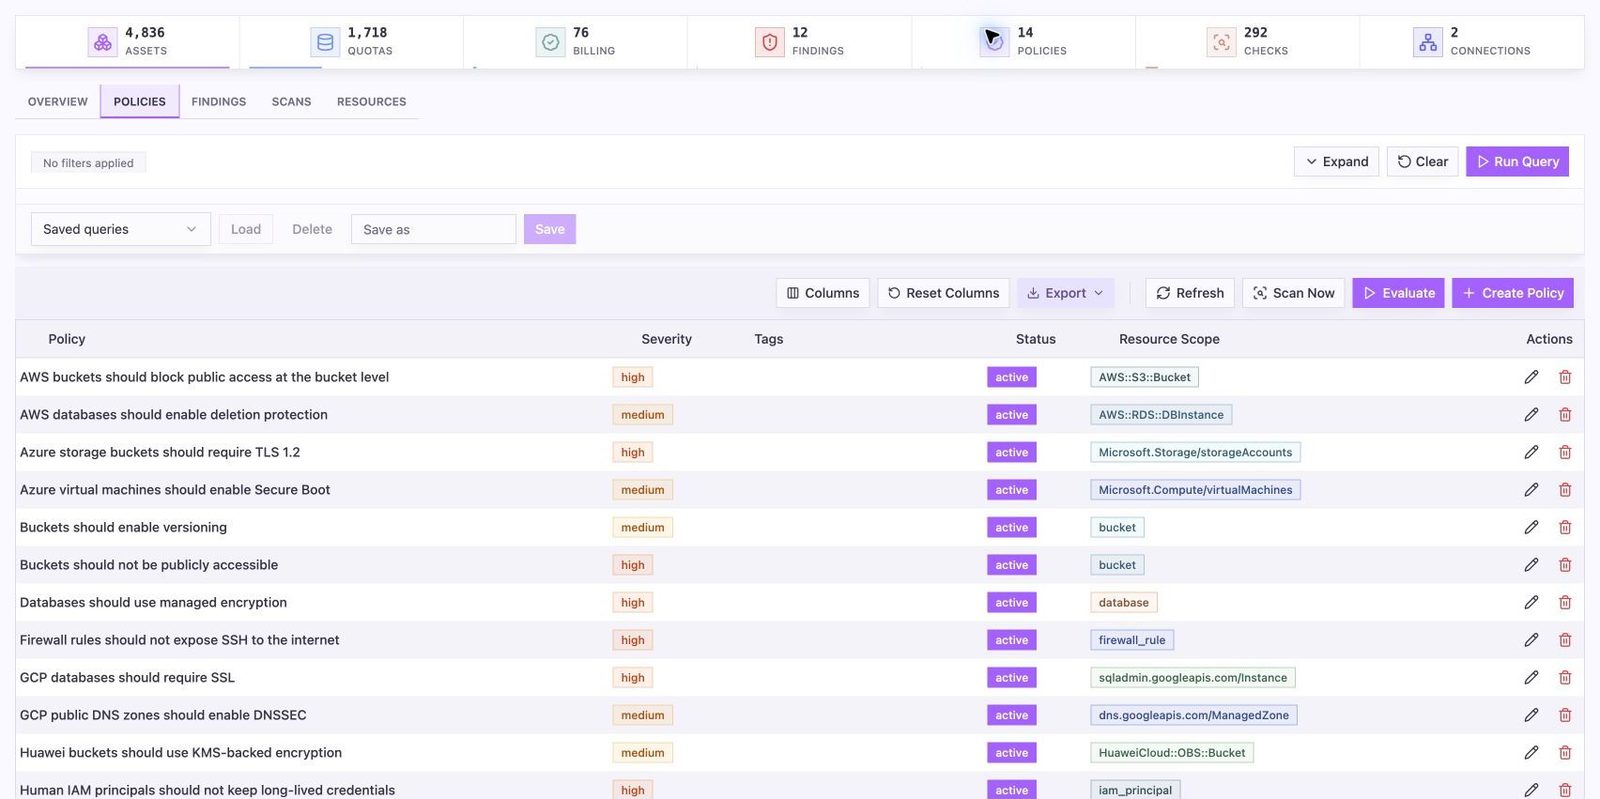
Find misconfigurations across AWS and Azure resources, from public exposure to encryption and access, with severity and resource context.
Capabilities
Accounts, regions and resources in a normalized inventory.
Access, encryption, network and public exposure controls.
Each finding shows the resource, account and the policy it violates.
Bring provider security findings into the same review flow.
Track control results over time for audits.
Add Cloud Operations and Cloud Automation to remediate from playbooks.
Built from Orbitron modules
Every Orbitron product is a set of platform modules on the same agent. Products you add later reuse the modules you already have.
 Cloud VisibilityVisibility · CLVIS
 Cloud SecuritySecurity · CLSEC
 Compliance ManagementSecurity · COMP
Optional add-ons
 Asset Visibility
 Alert Management
 Cloud Automation
 Cloud Management
 Command Engine
Licensing
Per billable cloud resource.
Annual subscription, priced for your environment. Products bought together share the modules they have in common.
Request pricingIncluded with every subscription
Works with
Book a demo and we will show it on infrastructure like yours.