Image and container risk
Vulnerability assessment for images and running containers.
Find vulnerable images before they ship, detect suspicious runtime behavior and isolate a single container when it matters. Licensed per vCPU, with automatic coverage of every container on a licensed node.
Capabilities
Vulnerability assessment for images and running containers.
Process and cgroup events mapped to containers and evaluated by detection rules.
Isolate one container without stopping the host.
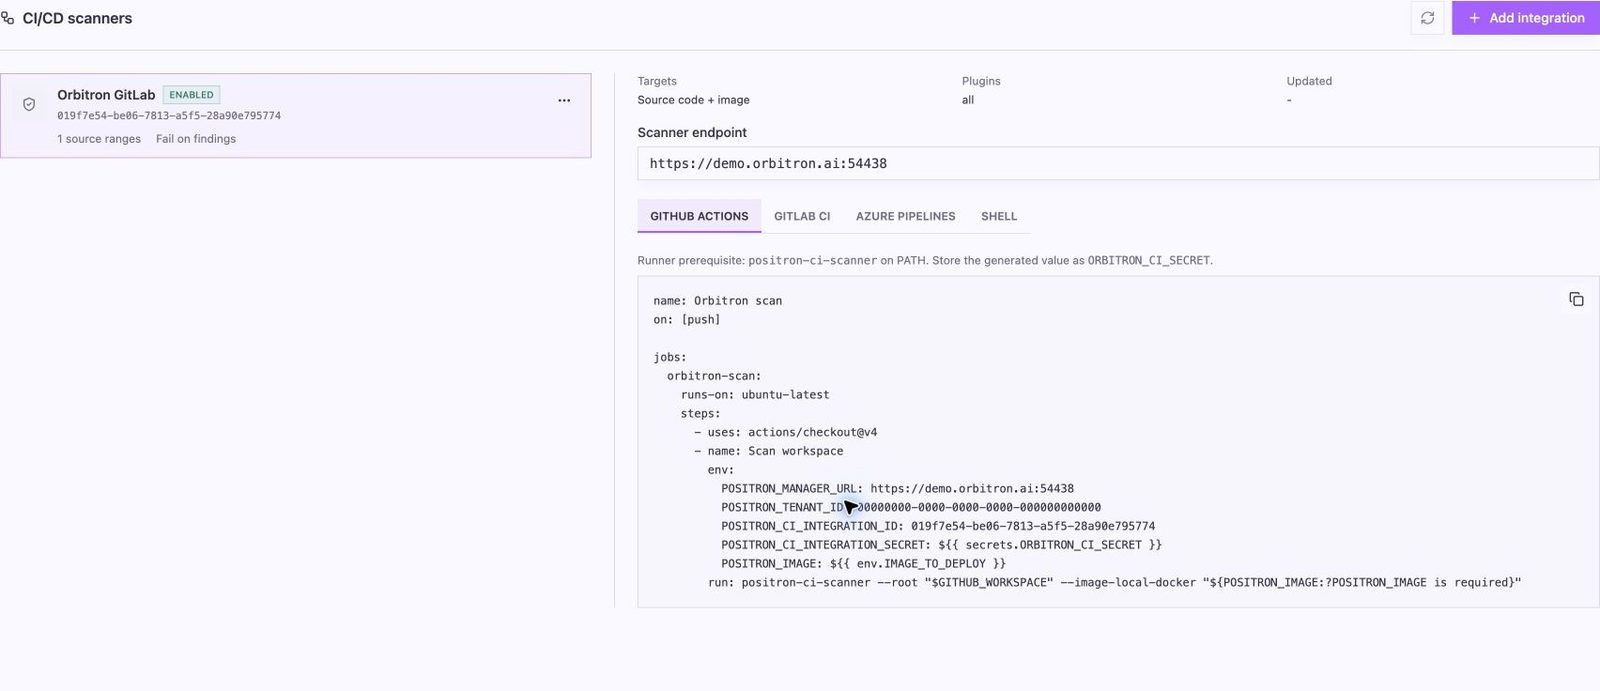
Pipeline templates for GitHub, GitLab and Azure with a fail-on-findings option.
CIS checks for Docker and Kubernetes configurations.
When a workload license is present, the agent starts covering containers and pods on its node.
Built from Orbitron modules
Every Orbitron product is a set of platform modules on the same agent. Products you add later reuse the modules you already have.
 Container VisibilityVisibility · CVIS
 Container SecuritySecurity · CSEC
 Vulnerability ManagementSecurity · VULN
 Rule Engine (Correlation)Security · CORR
 Alert ManagementSecurity · ALERT
 Command EngineAutomation · CMD
Optional add-ons
 Compliance Management
 Container Automation
 Container Management
Licensing
Per billable vCPU (minimum 4, maximum 16 per node).
Annual subscription, priced for your environment. Products bought together share the modules they have in common.
Request pricingIncluded with every subscription
Works with
 Cloud & ContainerOrbitron Container OperationsDocker, Kubernetes, K3s and OpenShift workloads in one operational view.
 Security OperationsOrbitron EDREndpoint detection, investigation and response, including container isolation.
 Cloud & ContainerOrbitron Cloud Security PostureMisconfigurations across AWS and Azure, ranked by severity.
Book a demo and we will show it on infrastructure like yours.